Benefits of ISO/IEC 42001 for Companies and Applicable Sectors
The use of Artificial Intelligence (AI) continues to grow across business activities. Therefore, organizations need a structured approach to manage AI-related risks, responsibilities, and opportunities. ISO/IEC 42001:2023 provides an Artificial Intelligence Management System (AIMS) framework to help organizations manage AI in a structured way. It covers key areas such as AI governance, AI risk management, […]
ISO 42001: Definition, Purpose, Benefits, and Implementation
The use of Artificial Intelligence (AI) is expanding across business processes, from automation to decision-making. However, AI also creates risks related to data, transparency, accountability, security, and governance. Organizations therefore need a structured approach to manage these risks and opportunities. ISO/IEC 42001 provides an Artificial Intelligence Management System (AIMS) framework that helps organizations manage AI […]
PCI DSS Compliance : Requirements, Assessment Process, and How to Prepare
PCI DSS compliance requires organizations to meet and validate the requirements of the Payment Card Industry Data Security Standard (PCI DSS) to protect payment account data. PCI DSS provides a baseline of technical and operational requirements for organizations that store, process, or transmit payment data. It also applies to entities that can impact the security […]
What Is PCI DSS? Definition, Objectives, and Benefits for Companies
Every organization that accepts, processes, stores, or transmits payment card data must protect that data. The global standard for payment account data protection is PCI DSS, or Payment Card Industry Data Security Standard. The PCI Security Standards Council (PCI SSC) develops and maintains this standard. What Is PCI DSS? According to the PCI Security Standards […]
PTBAE-PU: Managing Emissions through Emission Caps and Carbon Trading
Climate change encourages governments and businesses to not only measure Greenhouse Gas (GHG) Emissions, but also control the amount of emissions generated by business activities. In Indonesia, one of the instruments under the Carbon Economic Value (NEK) framework is the Technical Approval for Emission Caps for Business Actors (PTBAE-PU). PTBAE-PU establishes an emission cap for […]
Greenhouse Gases : Understanding GHG Emissions, Carbon Footprint, and Emission Reduction Strategies
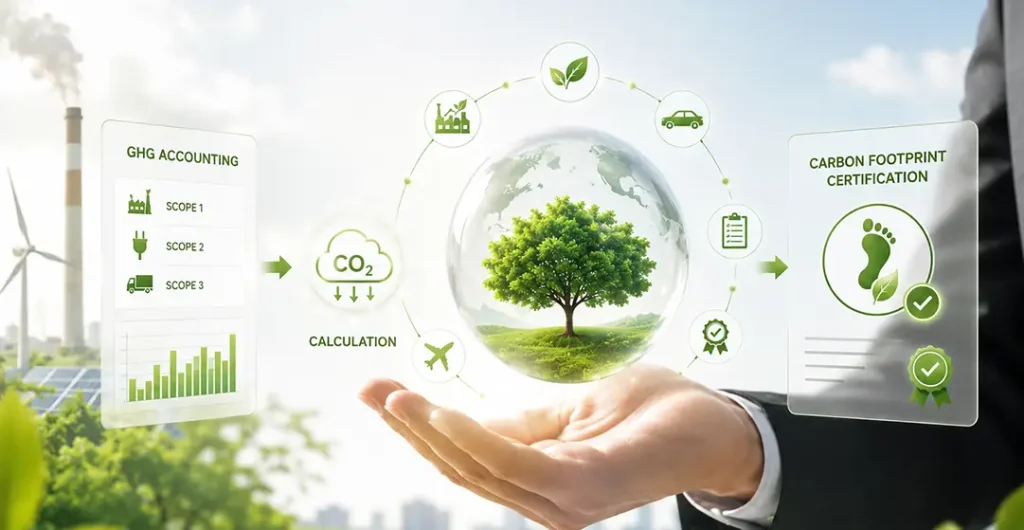
Climate change is increasingly driving organizations to understand and manage their environmental impact. As a result, GHG emissions have become an important part of sustainability management. For companies, managing GHG emissions involves more than calculating the amount of emissions they generate. Instead, emissions data can help organizations develop reduction strategies, improve operational efficiency, meet customer […]
SOC 2 Type 1 vs Type 2: Understanding the Differences and How to Choose
Executive SummarySOC 2 Type 1 vs Type 2 Understanding the Difference, Evidence, Operating Effectiveness & Readiness 1. Executive Overview SOC 2 Type 1 and Type 2 are both part of a SOC 2 examination based on the AICPA Trust Services Criteria. The main difference lies in the timing of the evaluation and the depth of […]
What Is SOC 2? Definition, Purpose, and Benefits for Companies
Executive SummaryProfessional & Insightful Summary 1. Overview What is SOC 2? SOC 2 is an examination framework based on the American Institute of Certified Public Accountants (AICPA) Trust Services Criteria (TSC). It helps evaluate the effectiveness of controls within a service organization. These controls support the management of systems and information related to Security, Availability, […]
GAP Audit ISO 9001:2026 : Assessing QMS Readiness
Is your company’s QMS ready for ISO 9001:2026? This question has become increasingly important since ISO published ISO 9001:2026 on 16 September 2026. The new edition replaces ISO 9001:2015 and provides updated requirements for quality management systems. However, organizations that already implement ISO 9001 do not need to build their Quality Management System (QMS) from […]
GAP Audit ISO 9001:2026: A Complete Guide to Transition Preparation
GAP Audit ISO 9001:2026 helps organizations that currently implement ISO 9001:2015 prepare for the transition to the latest edition. ISO 9001:2026 was officially published on 16 September 2026 and replaces ISO 9001:2015. The new edition maintains the core foundations of quality management. However, it places greater emphasis on leadership, quality culture, strategic alignment, risks, and […]