
SOC 2 Type I vs Type II: Which Should Your Business Choose First?
This question often comes up when a company enters the security review stage. The answer is not about which report carries more prestige. What matters most is choosing the right examination based on your company’s compliance objectives without paying for the process twice. What Is the Difference Between SOC 2 Type I and Type II? […]
What Is SOC 2, and Why Do Enterprise Clients Require It?
If your company provides SaaS or cloud services, or handles client data, you may receive a security questionnaire from a potential customer. Some enterprise clients may also ask a direct question: “Do you have a SOC 2 report?” SOC 2 (System and Organization Controls 2) is an attestation framework developed by the American Institute of […]
ISO/IEC 27001 vs SOC 2: Key Differences and How to Choose the Right Security Standard for Your Organization
In today’s digital era, data breaches and cyber threats have become major concerns across industries, from fintech and e-commerce to healthcare and cloud service providers. As a result, organizations face increasing pressure not only to secure their systems but also to demonstrate their commitment to information security to clients, regulators, and business partners. ISO/IEC 27001 […]
What Is an IT Audit and How Does It Protect Your Company’s Data?
As organizations rely increasingly on digital systems, protecting business information and maintaining reliable IT operations have become essential. However, technology also introduces risks related to cybersecurity, unauthorized access, system failures, data integrity, and regulatory compliance. An IT Audit helps organizations evaluate their information technology systems, processes, and controls. It identifies weaknesses, assesses whether controls operate […]
CBQA Global Underwent a KAN Surveillance Assessment as a LATIK to Support SPBE Audits
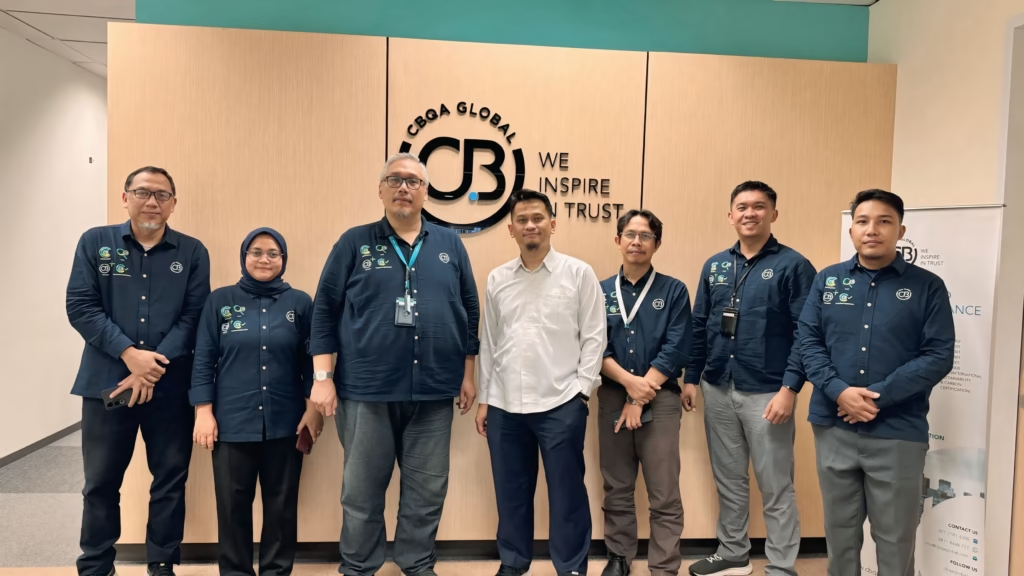
CBQA Global underwent a surveillance assessment by the National Accreditation Committee (KAN) on 5-6 October 2026. This assessment was part of the periodic monitoring of CBQA Global’s accreditation as a Lembaga Pelaksana Audit Teknologi Informasi dan Komunikasi (LATIK), or an Information and Communication Technology (ICT) Audit Implementing Institution. It also reviewed compliance with accreditation requirements […]
PCI DSS v4.0.1: Why It Matters as Cashless Transactions and Data Breach Risks Grow
The Rapid Growth of Digital Transactions vs. The Escalating Risk of Cardholder Data Breaches Digital transformation has significantly reshaped the business landscape. Across e-commerce, banking, financial technology (fintech), and retail, cashless payments have become essential to daily transactions. These options include credit cards, debit cards, and card-linked digital wallets. As transaction volumes rise, organizations also […]
Behind the Convenience of Digital Transactions: Assessing PJP System Readiness and Security
Millions of digital transactions take place in seconds every day. From scanning QRIS codes at a favourite coffee shop and transferring money between e-wallets to checking out online purchases through payment gateways, digital payments have pushed beyond the limits of conventional transactions. However, behind this speed and convenience lies a significant responsibility for Payment Service […]
CBQA Global Registered with ASPI as a Security Audit and Testing Service Provider
CBQA Global was officially registered with the Indonesian Payment System Association (ASPI) as a Security Audit and Testing Service Provider on 13 August 2026. This registration reinforces CBQA Global’s support for information technology security audits and compliance requirements in Indonesia. According to ASPI’s official list, PT CBQA GLOBAL INDONESIA holds Registration Certificate Number (STT) Sek.ASPI/STT/036/VIII/2026. […]
Threat and Vulnerability Risk Assessment (TVRA): What Financial Institutions Need to Know?
Financial Institutions are increasingly dependent on technology to deliver services and support daily operations. Therefore, technology risk management plays an important role in maintaining resilience and service continuity. Under the Technology Risk Management Guidelines (January 2021), the Monetary Authority of Singapore (MAS) provides principles and practices to help Financial Institutions establish technology risk governance and […]
What Is TVRA? Understanding Threat and Vulnerability Risk Assessment for Data Centres
Data Centres are critical infrastructure for organizations that rely on technology-based services. Any disruption to facilities, infrastructure, or supporting systems can affect service availability and business operations. One approach outlined in the Monetary Authority of Singapore (MAS) Technology Risk Management Guidelines is Threat and Vulnerability Risk Assessment (TVRA). In the context of Data Centres, TVRA […]