Behind the Convenience of Digital Transactions: Assessing PJP System Readiness and Security
Millions of digital transactions take place in seconds every day. From scanning QRIS codes at a favourite coffee shop and transferring money between e-wallets to checking out online purchases through payment gateways, digital payments have pushed beyond the limits of conventional transactions. However, behind this speed and convenience lies a significant responsibility for Payment Service […]
The Urgency of Personal Data Protection in the Healthcare Sector
In today’s digital era, easier access to personal data creates serious challenges, especially in healthcare. Digital healthcare services improve access to information. However, they also increase the risk of exposing sensitive patient data. Hospital information systems, electronic medical records, and healthcare applications can become targets for cybercriminals. ISO/IEC 27701 can support a structured approach to […]
PP 33 of 2026: Personal Data Protection Requirements for Organizations
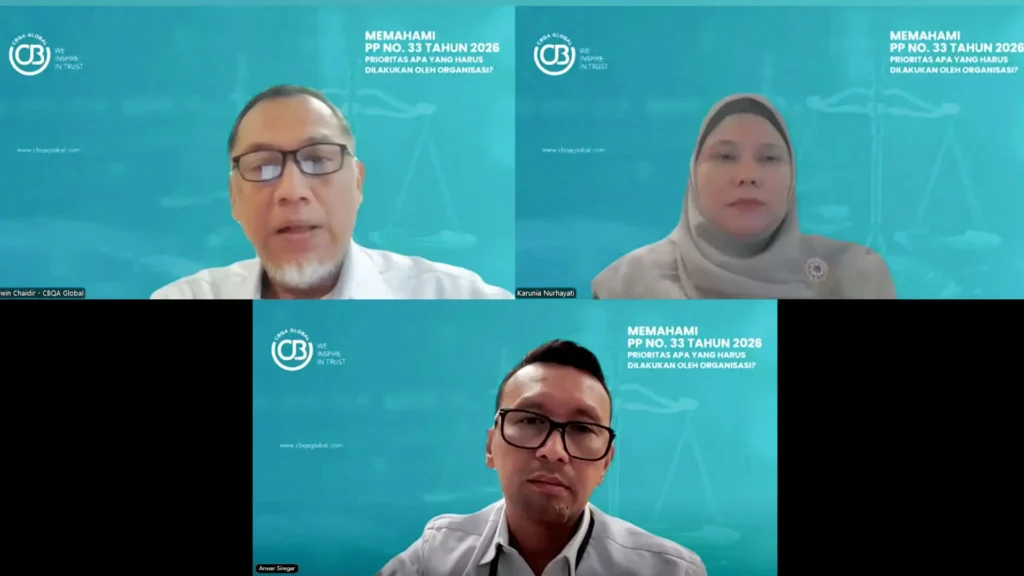
PP No. 33 of 2026 provides implementing requirements for Personal Data Protection (PDP) in Indonesia. The regulation supports the implementation of Law No. 27 of 2022 on Personal Data Protection and provides a more operational framework for organizations. This topic was discussed in the CBQA Global webinar, “Understanding PP No. 33 of 2026: What Should […]
CBQA Global Asia Pacific Director Shares ISO/IEC 27001 Insights at Research Security and Cyberbiosecurity Workshop for Indonesian Biotechnology Companies
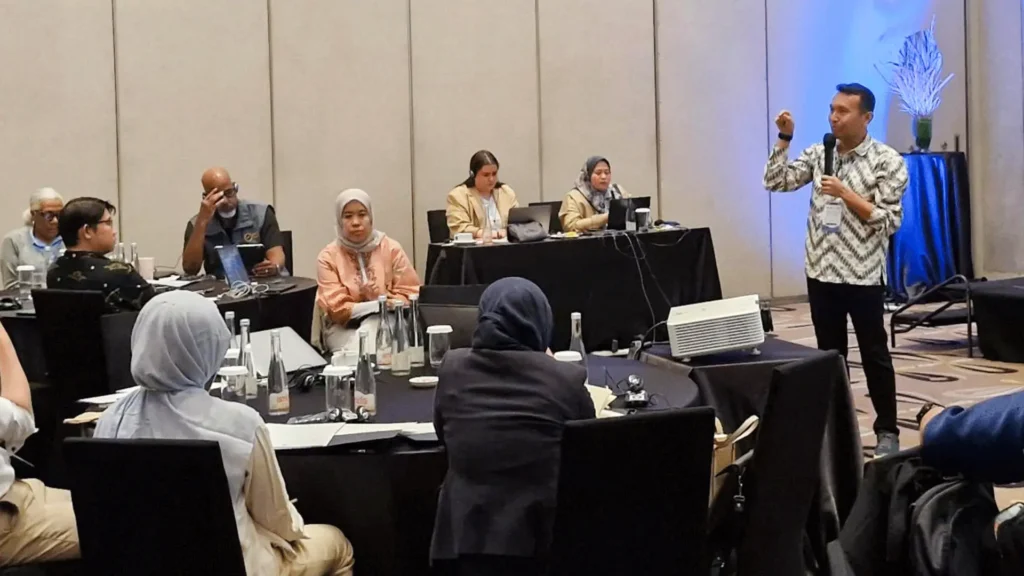
Jakarta, 22 September 2026 – Anwar Siregar, Director Asia Pacific at CBQA Global, was invited as a speaker at the Raising Awareness on Research Security and Cyberbiosecurity Best Practices for Indonesian Biotechnology Companies workshop. The workshop was held in Jakarta on 22-23 September 2026. The two-day workshop was initiated by Health Security Partners (HSP). It […]