CBQA Global Undergoes ISO/IEC 27701 Accreditation Surveillance by KAB to Improve PIMS Certification Quality
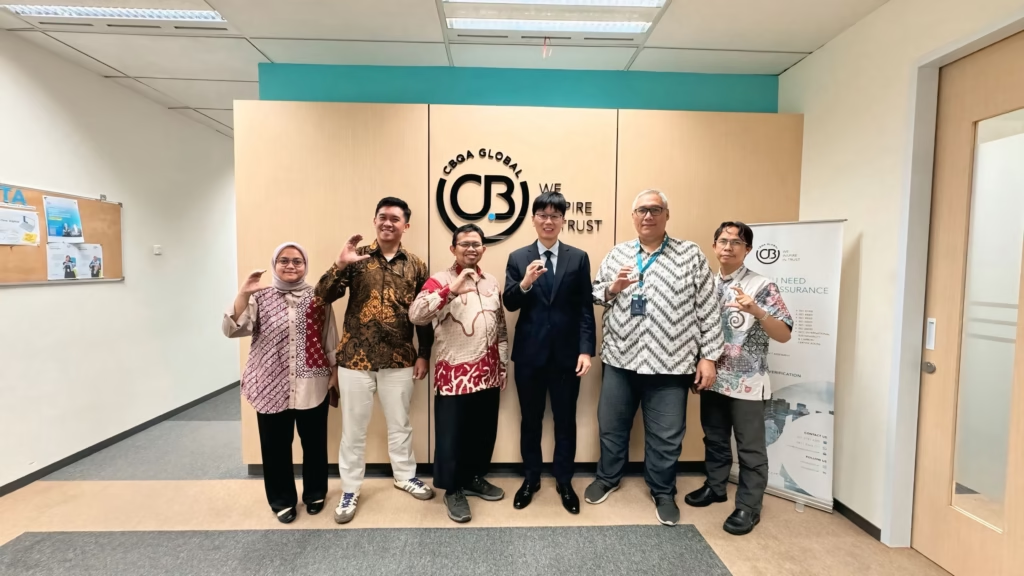
CBQA Global underwent an accreditation surveillance assessment conducted by Korea Accreditation Board (KAB) for ISO/IEC 27701. The assessment aims to review the consistency of Privacy Information Management System (PIMS) certification processes and ensure that they remain aligned with the applicable standards and requirements. The assessment also provides CBQA Global with an opportunity to receive feedback […]
What Is ISO 27701 Certification? Benefits, Process, and Its Relationship with Indonesia’s PDP Law
ISO 27701 certification demonstrates that a Privacy Information Management System (PIMS) conforms to the requirements of the ISO/IEC 27701 standard. This standard helps organizations manage personal information systematically, strengthen accountability, and control data privacy risks. According to the International Organization for Standardization (ISO), ISO/IEC 27701 specifies requirements for “establishing, implementing, maintaining, and continually improving a […]
What Is ISO 27701 Training? Course Content, Benefits, and Who Should Attend
ISO 27701 Training helps professionals understand how to plan, conduct, and lead audits of a Privacy Information Management System (PIMS). CBQA Global’s Lead Auditor Course (LAC) for ISO/IEC 27701:2025 aims to develop auditing competencies for privacy information management systems based on the latest standard requirements. According to the International Organization for Standardization (ISO), ISO/IEC 27701:2025 […]
The Urgency of Personal Data Protection in the Healthcare Sector
In today’s digital era, easier access to personal data creates serious challenges, especially in healthcare. Digital healthcare services improve access to information. However, they also increase the risk of exposing sensitive patient data. Hospital information systems, electronic medical records, and healthcare applications can become targets for cybercriminals. ISO/IEC 27701 can support a structured approach to […]
Importance of Privacy and the Role of ISO/IEC 27701 Certification in Protecting Personal Data
What Does Privacy Mean? Privacy means having the right to be left alone and free from unwanted intrusion. In information privacy, it also means having control over who collects your personal data, how they process it, and how they use it. Today, people often associate privacy with data breaches, smartwatches, social media, and online ads […]
PP 33 of 2026: Personal Data Protection Requirements for Organizations
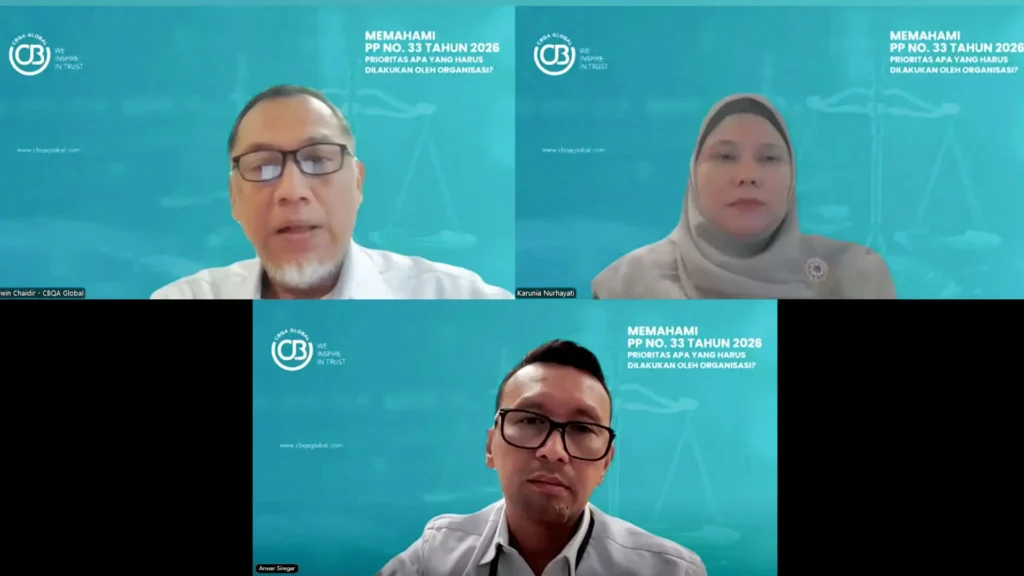
PP No. 33 of 2026 provides implementing requirements for Personal Data Protection (PDP) in Indonesia. The regulation supports the implementation of Law No. 27 of 2022 on Personal Data Protection and provides a more operational framework for organizations. This topic was discussed in the CBQA Global webinar, “Understanding PP No. 33 of 2026: What Should […]
A New Era of Personal Data Protection: PP 33/2026 and the Vital Role of a Personal Data Protection Officer
The Government of Indonesia has officially enacted Government Regulation No. 33 of 2026 (PP 33/2026) as the implementing regulation of Law No. 27 of 2022 on Personal Data Protection (PDP Law). This regulation provides more detailed requirements covering the personal data processing lifecycle, from collection to destruction, as part of efforts to protect and safeguard […]