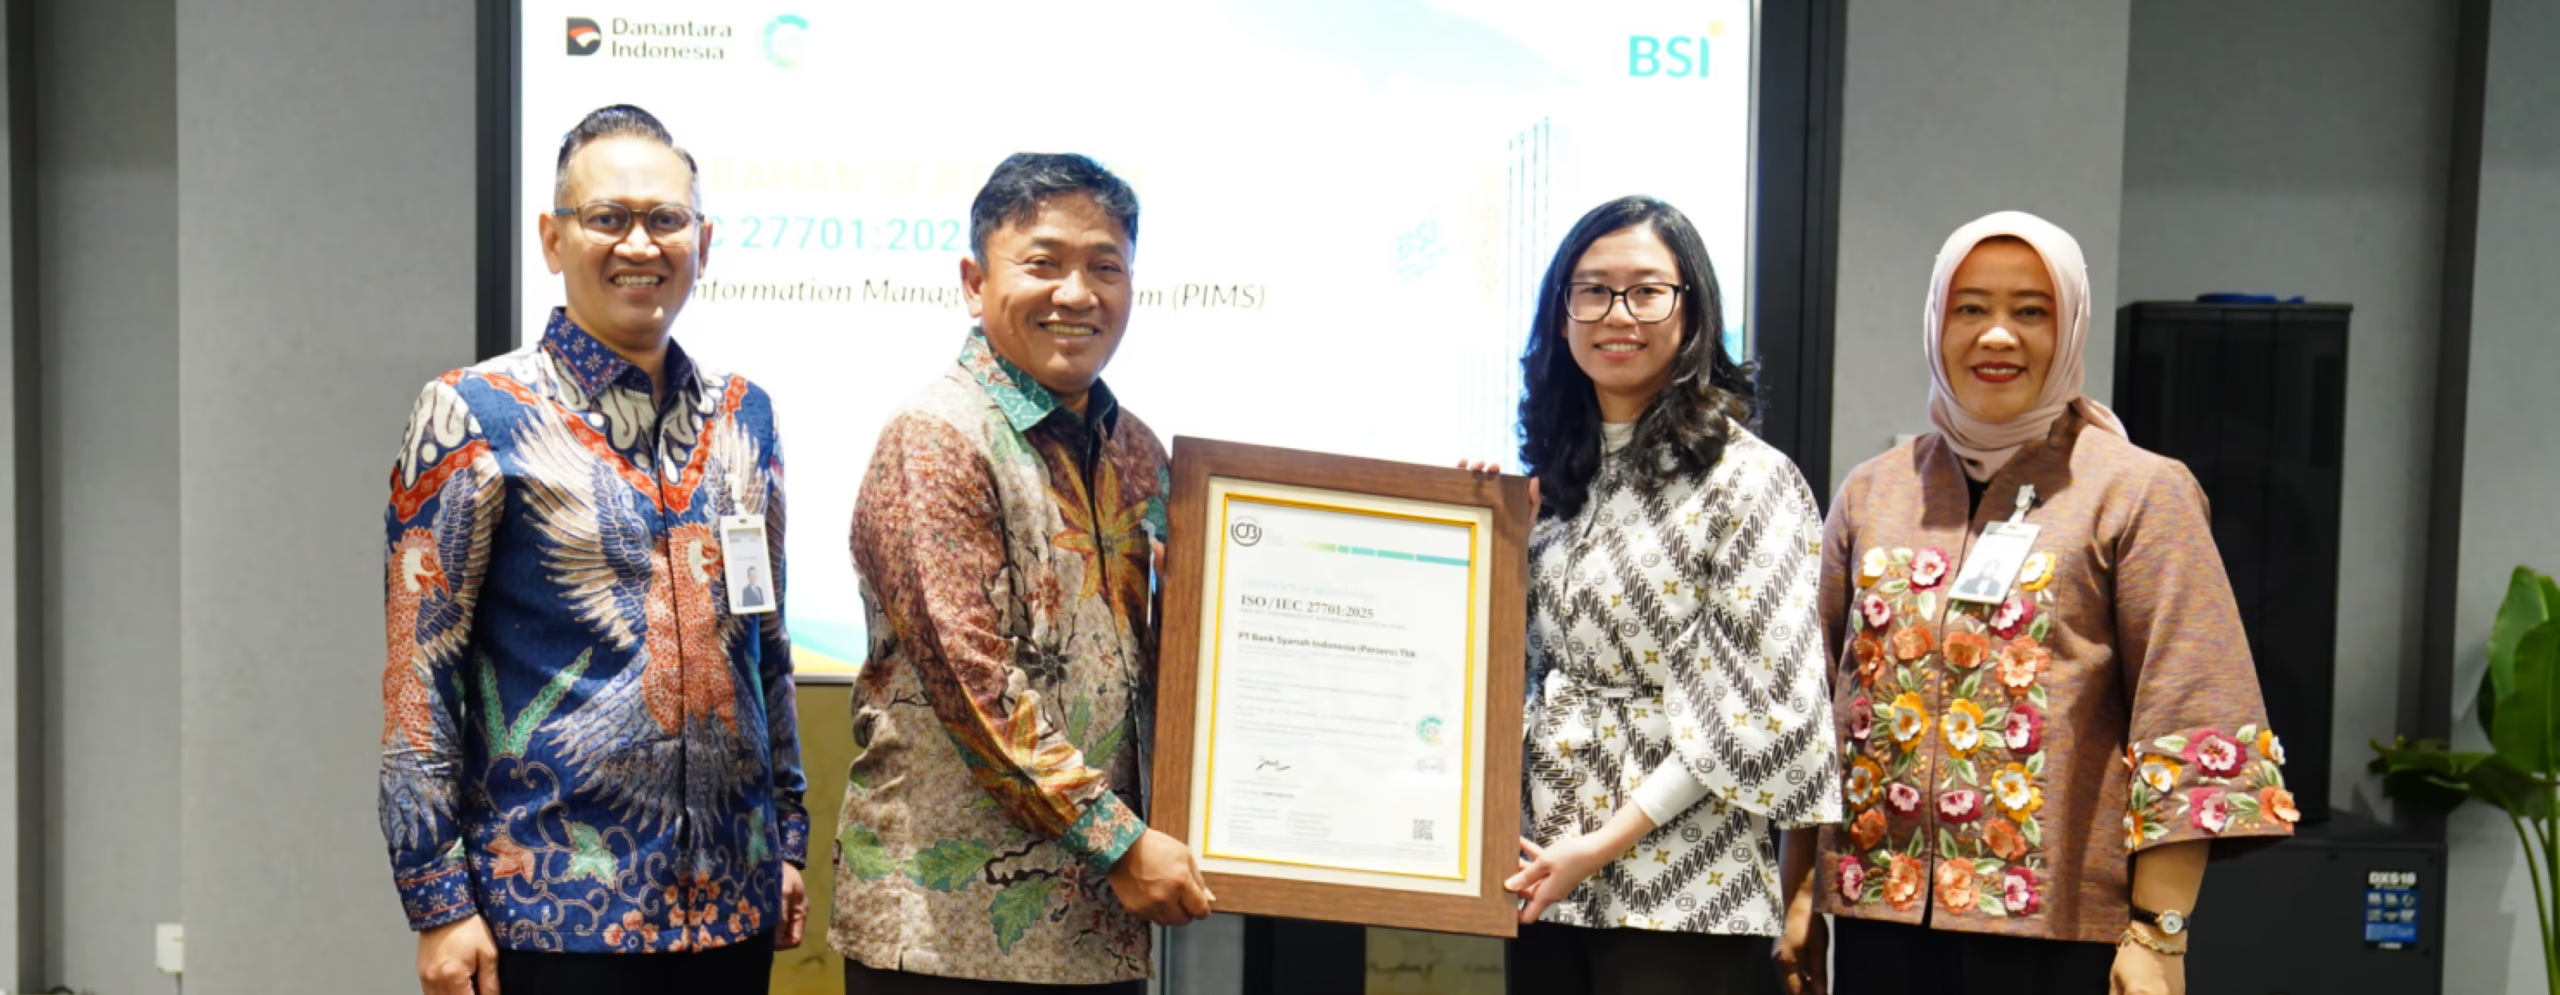
Jakarta, September 17, 2026 – CBQA Global marked an important milestone in strengthening privacy governance and data protection in Indonesia’s banking industry through the presentation of ISO/IEC 27701:2025 certification to PT Bank Syariah Indonesia (Persero) Tbk (BSI). The certification relates to the implementation of a Privacy Information Management System (PIMS).
During the certificate presentation ceremony, Mrs. Yessiva as President Director of CBQA Global, was present alongside representatives of BSI. The certificate presentation marks a shared commitment to promoting more structured, measurable, and sustainable privacy governance and personal data protection.
What Is ISO/IEC 27701:2025?
ISO/IEC 27701:2025 is an international standard that specifies requirements for establishing, implementing, maintaining, and continually improving a Privacy Information Management System (PIMS).
The standard is intended for organizations responsible for processing personally identifiable information (PII), enabling privacy management to be carried out in a more structured, accountable, and risk-based manner.
Why Is ISO/IEC 27701:2025 Important for BSI?
For CBQA Global, BSI’s achievement represents an important step in strengthening data privacy governance, while also supporting the strategic transformation of Badan Pengelola Investasi Daya Anagata Nusantara (Danantara) Indonesia in building globally competitive national financial institutions.
BSI stated that this achievement is part of its commitment to continuously deliver services that prioritize customer trust and data protection.
Why Is ISO/IEC 27701:2025 Important for BSI?
The ISO/IEC 27701:2025 certification covers two key service areas that play an important role in BSI’s digital interaction with customers: the BYOND by BSI super app and Customer Care services.
According to information provided by BSI, this service ecosystem supports more than 24 million customers and recorded more than 400 million BYOND transactions as of June 2026.
BSI’s Commitment to Customer Data Privacy
BSI Deputy President Director Bob T Ananta emphasized the importance of managing customer data privacy through security standards that are measurable and sustainable. According to BSI, the ISO/IEC 27701:2025 certification is not only related to regulatory compliance, but also forms part of its efforts to maintain public trust in digital banking services.
BSI also views its ISO/IEC 27701:2025 achievement as a commitment to continuously strengthen personal data protection. In the banking environment, protecting customer information is an important part of service quality, transparency, security, and customer trust.
Furthermore, BSI explained that customer data protection has become part of the company’s work culture through its EMAS values, which stand for Empathy, Serving, Enthusiasm, and Wholeheartedness. This commitment is implemented not only through direct customer service, but also through stronger digital protection and data governance within the cyber environment.
Data Protection as Part of Corporate Culture
Technically, the implementation of ISO/IEC 27701:2025 within BYOND by BSI incorporates a privacy-by-design approach, strict access controls, privacy risk mitigation, and continuous monitoring.
Meanwhile, within Customer Care services, identity verification and the fulfillment of customer data subject rights are managed in accordance with international practices for privacy information management.
The strengthening of privacy governance and data security also contributes to the overall customer service experience. BSI stated that the institution ranked second in the 2026 Bank CX Tracker, which it described as one reflection of its focus on customer experience and trust.
BSI Director of Compliance & Human Capital, Arief Adhi Sanjaya, stated that the ISO/IEC 27701:2025 certification is not the end point. Instead, the certification represents a strategic step toward continuously improving privacy governance and information security across BSI’s service ecosystem, including through the development of human capital capabilities and a stronger data protection culture throughout the organization.
The Role of ISO/IEC 27701:2025 in Strengthening Privacy Governance
Through ISO/IEC 27701:2025 certification, BSI strengthens its commitment to privacy information governance in supporting digital transformation and maintaining customer trust.
From CBQA Global’s perspective, this achievement highlights the importance of implementing a structured privacy management system to help organizations manage privacy risks, strengthen accountability, and build stakeholder trust.
CBQA Global and ISO/IEC 27701:2025 Certification
As a Certification, Audit, Training, Verification & Validation organization, CBQA Global provides services related to Privacy & Data Protection, including ISO/IEC 27701:2025 certification.
CBQA Global has also announced the availability of ISO/IEC 27701:2025 certification accredited through the Korea Accreditation Board (KAB) to support organizations in implementing the latest standard for privacy information management.
Build a More Structured Privacy Management System with CBQA Global
Today, personal data management is no longer limited to information security. It also involves accountability, privacy governance, compliance, risk management, and customer trust.
ISO/IEC 27701:2025 provides an international framework to help organizations establish and continually improve their Privacy Information Management System (PIMS).
CBQA Global can help organizations understand their readiness, requirements, and implementation of ISO/IEC 27701:2025 based on their business context and personal data management needs.
Want to Know Your Organization’s Readiness for ISO/IEC 27701:2025?
Contact CBQA Global to learn more about ISO/IEC 27701:2025 Certification, Privacy & Data Protection, Gap Assessment, and services related to privacy governance and information management.
CBQA GLOBAL
Certification | Audit | Training | Sustainability
Email: info@cbqaglobal.com
WhatsApp: 08118468777
Phone: +62 21 2781 4200